Optimizely Attack Reveals a Software Supply Chain Security Gap
LinuxSecurity linuxsecurity.com
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.Malicious code was injected into websites using Optimizely's Web Experimentation service.
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
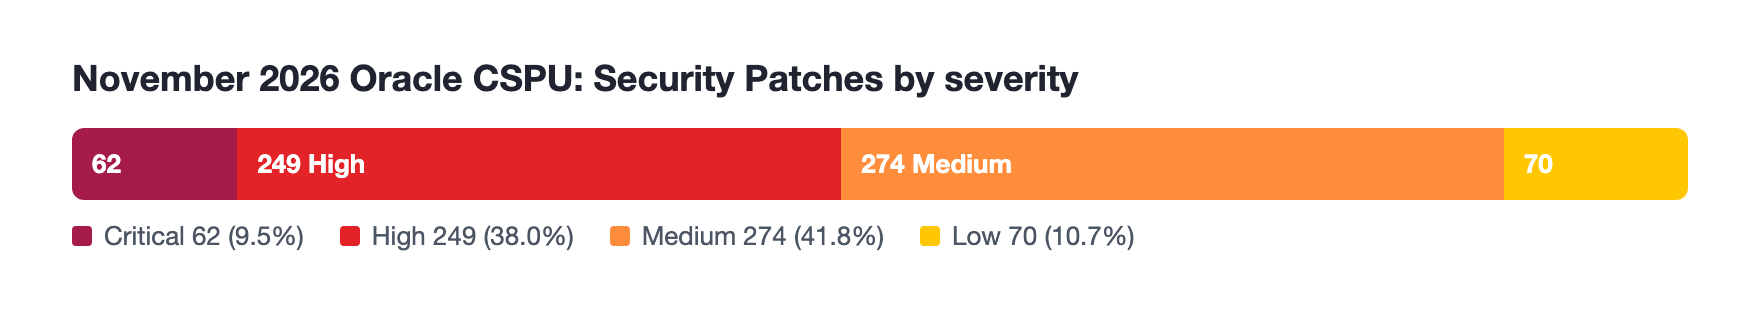 Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)
 U.S. urges critical infrastructure orgs to secure refrigeration systems ASAP after EU supermarket and blood bank attacks